Activity
Mon
Wed
Fri
Sun
Nov
Dec
Jan
Feb
Mar
Apr
May
Jun
Jul
Aug
Sep
What is this?
Less
More
AI Automation Mastery
30.2k
Free
The AI/GRC Career Starter
636
Free
CISSP Study Group
2.4k
Free
CyberMAYnia CAREER
596
Free
13 contributions to CISSP Study Group

Jul 2 •
CISSP Practice Question (Domain 5: Identity and Access Management - AI Exam Guidance)
An AI scheduling agent needs calendar and email access for all executives. The vendor requests a single privileged service account to simplify deployment before next month's rollout deadline. As the IAM lead, what is the MOST appropriate action? A. Approve the account with session recording enabled B. Issue scoped non-human identities per function with credential rotation C. Delay rollout until the vendor supports federated authentication D. Grant access but restrict it to business hours only Come back for the answer tomorrow, or study more now!
1 like • Jul 2
B. Issue scoped non-human identities per function with credential rotation
Apr 23 •
CISSP Practice Question (Domain 1: Security and Risk Management - Third-Party Risk)
Your SaaS CRM vendor notifies you that a subprocessor they rely on for email delivery suffered a breach. Your customer contact data was likely exposed. The vendor cannot yet confirm scope or timeline. What should the CISO do FIRST? A. Notify affected customers within 72 hours to meet GDPR deadlines B. Trigger the incident response plan and engage legal counsel on breach notification obligations C. Terminate the contract with the CRM vendor for failing to secure its supply chain D. Demand the subprocessor provide forensic evidence directly to your security team Come back for the answer tomorrow, or study more now!
2 likes • Apr 23
Although Forensic evidence is still important, but in terms of priority triggering the incident response plan comes first. so answer is B
Apr 10 •
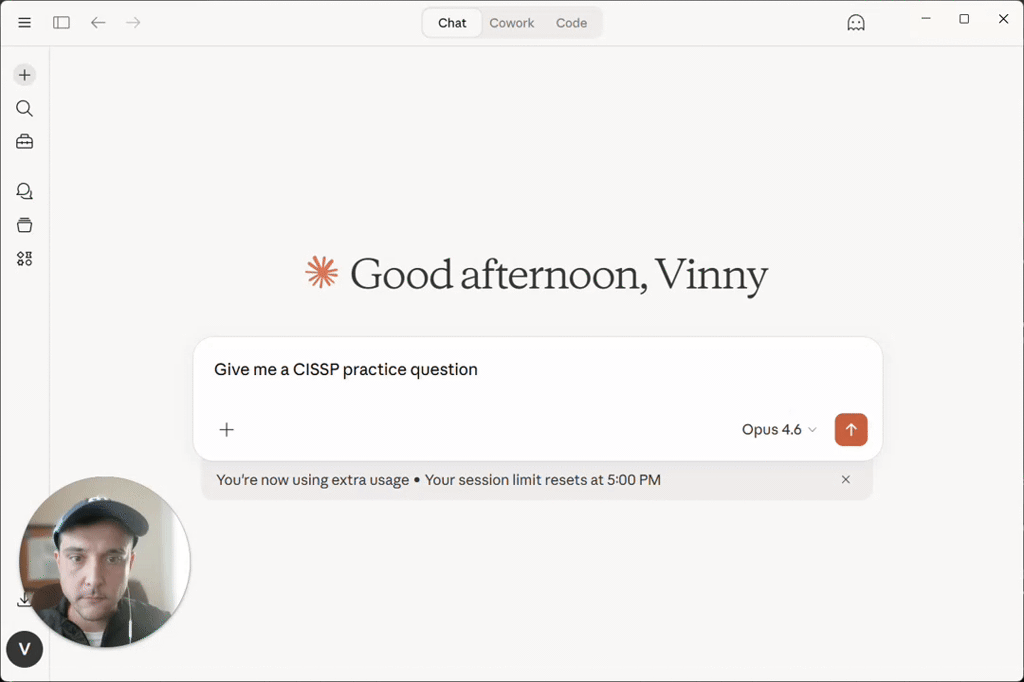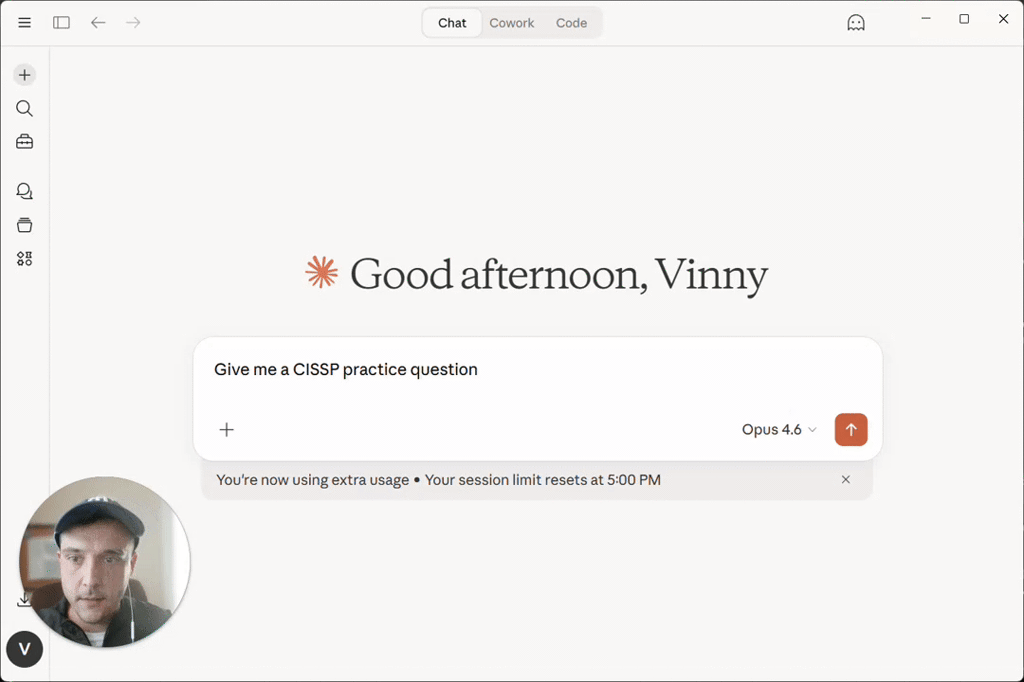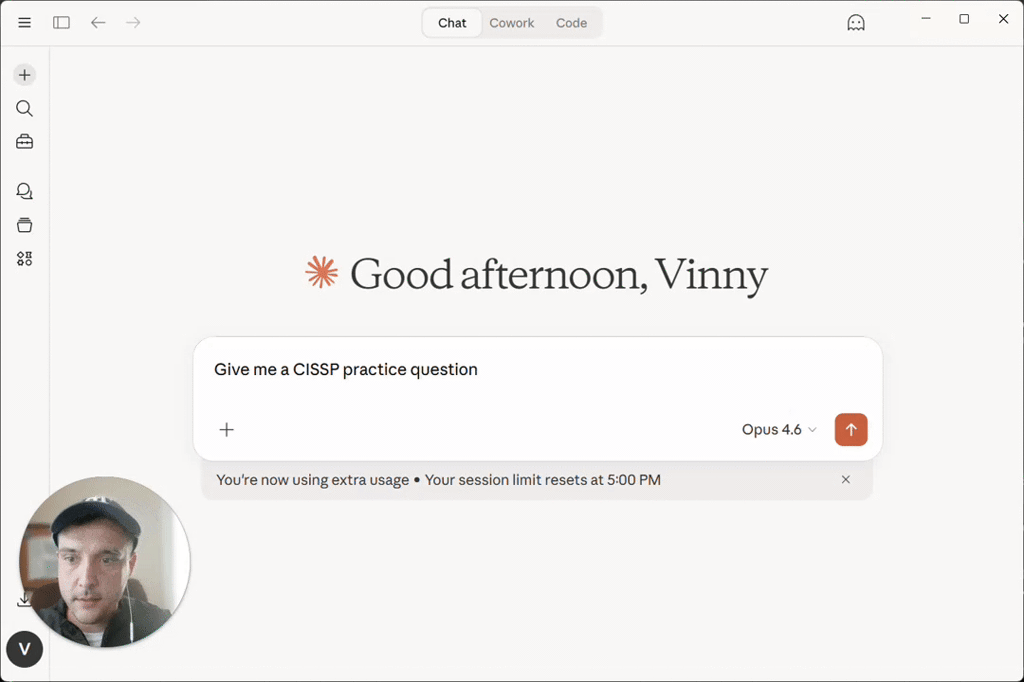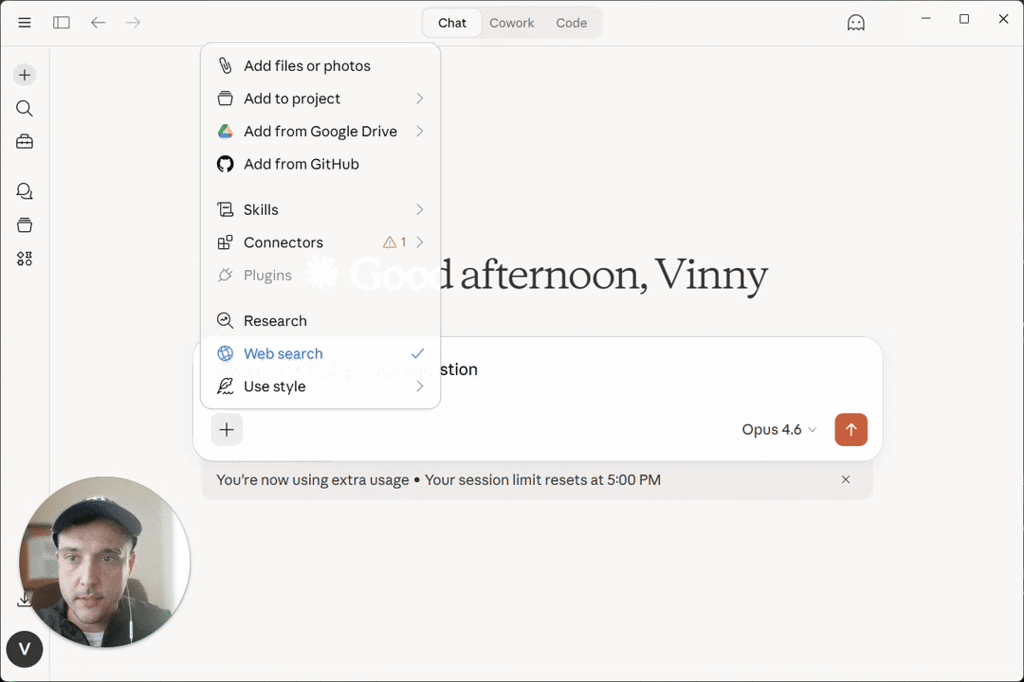
Chat with Claude about YOUR cissp.app stats and exam readiness
You can now access our 3,600+ CISSP practice questions, as well as YOUR personal data from cissp.app directly inside Claude. Correct / incorrect answers, mock exams taken, even the amount of time spent per question, you can get all that fed to Claude for better analysis on your data. Ask it to quiz you, check your answers, and get the same Manager Logic explanations you're used to from cissp.app without leaving your AI chat. cissp.app subscribers get unlimited questions plus your personal study stats, weak area analysis, and exam readiness scoring right inside Claude. We're the first and only CISSP prep tool that has this. How to set it up (30 seconds): 1. Open Claude at claude.ai (free account works) 2. Click the hamburger menu → Settings → Connectors 3. Click "Add" and paste this URL: https://cissp-mcp-server.cissp.workers.dev/mcp 4. Done. Start chatting. Examples of what you can ask: - "Give me a hard CISSP question about access control" - "Quiz me on Domain 4 — Network Security" - "I think the answer is B" (it checks and explains why) - "What are my weakest CISSP domains?" (subscribers) - "Am I ready for the exam?" (subscribers) Try it and let me know what you think in the comments.
0 likes • Apr 15
What are the paid subscription models that we have for CISSP app?
Feb 16 •
CISSP Practice Question (Domain 6: Security Assessment and Testing)
Your organization completed a penetration test that found critical vulnerabilities in a payment processing system. The business unit owner wants to delay remediation until after the holiday revenue peak, citing potential downtime. What should you do FIRST? A. Override the business unit and enforce immediate remediation of all critical findings B. Escalate to the risk committee with a temporary compensating controls proposal C. Accept the delay since the business unit owner is the risk owner D. Commission a follow-up penetration test to validate exploit feasibility Come back for the answer tomorrow, orstudy more now!
1 like • Feb 16
B. Escalating to Risk Committee with temp compensating control seems to be the best thing to do FIRST
Feb 14 •
CISSP Practice Question (Domain 2: Asset Security)
Your organization classifies data into four tiers, but a recent audit reveals that 60% of assets remain unclassified because data owners dispute classification responsibility with IT custodians. What should you do FIRST? A. Default all unclassified assets to the highest classification tier B. Assign IT custodians temporary classification authority to eliminate the backlog C. Clarify data ownership roles and accountability in the classification policy D. Implement automated classification tools to remove the human bottleneck Please share your thinking, I'd really like to know how everyone looks at this very real world scenario. Come back for the answer tomorrow, or study more now!
0 likes • Feb 16
First step is to check /clarify what the policy directs! So I Choose C
1-10 of 13
@gideon-manoharan-1986
GRC tech/Cyber Controls Management. Working for Deloitte internal services. I enable GRC controls onboarding and automating, modernizing GRC processes
Active 8h ago
Joined Jan 29, 2026
Powered by